
Healthcare Security and PHI Protection Built for Real-World Compliance
Digital Scientists builds and runs healthcare platforms that handle PHI under a signed BAA. NeverAlone, the virtual care platform we've operated 24/7 since March 2021, supports 30,000 patients across six states. Every engagement with PHI starts with a BAA. Our security plan is mapped to NIST CSF 2.0, and each client gets a security addendum. We're open about what we don't hold: no SOC 2, no HITRUST. On new builds, AI runs in your own AWS account, with a person approving every output. Talk it over with us, and we'll send the diligence packet.
Updated

NeverAlone live with PHI, 24/7
Patients across six states on NeverAlone
Signed before any PHI moves or system access is granted
Security plan mapping, plus a security addendum per client
Has Digital Scientists protected PHI in a live clinical platform?
Yes. We've run NeverAlone, a 24/7 virtual care platform for CommuniCare, since March 2021. It handles PHI every hour of every day, so our controls get tested by real use.
NeverAlone began as a 90-day MVP. It now supports 30,000 patients across six states, with 100,000+ calls a year on 750+ managed iPads. The platform pulls resident data from PointClickCare and Netsmart (GEHRIMED), runs video on AWS Chime and routes emergency calls through Bandwidth E911. Each of those is a place where PHI moves, and each one sits under a BAA, encryption and access logging.
That's why our PHI protection services start from production. Running platforms keeps us grounded in the challenges of everyday care delivery. We applied the same controls to CommuniCare's MDS platform, built from April 2024 on PointClickCare data and handed to CommuniCare's own team, and to Guardian, where vital signs stream from operating room devices into an AWS environment hardened with WAF, GuardDuty and CloudTrail. See the NeverAlone case study.
NeverAlone live with PHI, 24/7
Patients across six states
Calls a year
Managed devices under MDM
Where we stand today
Transparency is the starting point. Here is our current compliance status: what we have in place, and what we don't hold.
HIPAA Compliance
We operate as a HIPAA-compliant business associate. Our security controls, workforce training, and data handling practices meet the HIPAA Security Rule, Privacy Rule, and Breach Notification Rule. We execute a BAA with every covered entity and subcontractor, no exceptions.
SOC 2
We don't hold a SOC 2 report, and SOC 2 isn't on our roadmap. What we do instead: a BAA with every covered entity, a security plan mapped to NIST CSF 2.0, and a security addendum written for each client's project.
HITRUST CSF
We do not hold HITRUST certification, and it isn't on our roadmap.
How the program runs: Our security plan is a written information security program with a HIPAA annex, mapped to NIST CSF 2.0. Policies live in a governed compliance portal, a control register tracks each control with its owner and evidence, and each client's project gets a security addendum for anything specific to that work.
Our BAA process
Every engagement that involves PHI starts with an executed BAA. Here is how we handle it.
Scope Review
We assess whether the engagement involves PHI or ePHI. If it does, or could, we initiate a BAA before any data is exchanged or system access is granted.
Agreement Execution
We work with your legal and compliance teams to execute a BAA that defines permitted uses, disclosure limitations, safeguard obligations, and breach notification requirements.
Subcontractor Chain
We maintain BAAs with our own vendors and subcontractors who may access PHI, covering the entire chain of custody, including cloud infrastructure providers like AWS and Azure.
Ongoing Obligations
BAAs are not filed and forgotten. We conduct periodic reviews and maintain documentation of our compliance posture throughout the engagement, and after data return or destruction.
People, policies, and governance
Technical controls are only as strong as the people and processes behind them. Our administrative safeguards address workforce security, risk management, and incident readiness.
Security Risk Analysis
We conduct periodic security risk analyses to identify threats to ePHI. Findings feed into our risk register, where each risk is scored, assigned an owner, and tracked through mitigation. Risk assessments are repeated annually and after significant system changes.
Workforce Training
All team members complete HIPAA Security and Privacy awareness training at onboarding and annually thereafter. Training covers PHI handling, breach identification, social engineering, and reporting obligations.
Security Policies & Governance
Our information security policies are documented, version-controlled, reviewed annually, and published in our compliance portal. All team members acknowledge policies and updates in writing. Governance includes defined roles, accountability, and regular compliance reviews.
Incident Response
We maintain a documented incident response plan that meets HIPAA Breach Notification Rule requirements. Real-time monitoring identifies potential incidents. Critical incidents are escalated within one hour. If a breach of PHI is confirmed, we notify affected covered entities within BAA-specified timeframes, well within the HIPAA 60-day window. Every incident concludes with a blameless post-mortem and tracked remediation actions.
Background Screening
We conduct background screening for all personnel who will have access to PHI or client systems, consistent with the sensitivity of the data and access level involved.
Onboarding & Offboarding
New team members complete security training and policy acknowledgment before receiving any system access. When team members leave an engagement or the company, access is revoked within 24 hours. Documented checklists cover device return, credential revocation, and access audit verification.
Track record: Digital Scientists has had no reportable breach of protected health information. We log every security incident, including ones where no PHI was exposed, and walk your security team through that history in diligence.
Proven in production: These are not theoretical controls. We maintain incident readiness for NeverAlone, our EHR-integrated clinical platform used 24/7 by 30,000 patients across six states since March 2021, where uptime, data integrity, and security directly impact patient care.
Security built into every layer
From encryption and access control to automated testing and continuous monitoring, our technical safeguards protect ePHI throughout its lifecycle.
Encryption
All ePHI is encrypted at rest using AES-256 and in transit using TLS 1.2 or higher. Encryption keys are managed through cloud-native key management services (AWS KMS, Azure Key Vault) with automatic rotation and access-logged key usage.
Access Control
We enforce role-based access control (RBAC) with the principle of least privilege. Access to PHI requires multi-factor authentication (MFA). All access is logged, and we conduct quarterly access reviews to verify entitlements match current roles.
Audit Logging
Immutable audit trails capture all access to PHI, who accessed what, when, and from where. Logs are centrally aggregated and retained according to HIPAA-compliant retention policies.
Data Minimization
We collect and process only the minimum PHI necessary for the engagement. Development and testing use de-identified or synthetic data sets. Production PHI access is reserved for validated environments only.
Secure SDLC
Security requirements are defined during discovery and validated at every stage: design reviews, threat modeling, code reviews, automated testing, and pre-deployment security gates.
Automated Security Testing
SAST and DAST run in CI/CD pipelines. Dependency scanning flags known vulnerabilities in third-party libraries before they reach production.
Code Review & Pen Testing
All code changes are peer-reviewed with security-specific criteria. No code merges to production without an approved review. We conduct regular penetration testing using both internal assessments and third-party firms.
Intrusion Detection & SIEM
We deploy network and host-based IDS, SIEM for centralized log analysis, and real-time alerting. Anomalous access patterns trigger automated investigation workflows.
Vulnerability Management
Continuous vulnerability scanning of infrastructure and application layers. Critical findings are triaged within 24 hours and patched according to severity-based SLAs.
Cloud-native, healthcare-hardened
We build on HIPAA-eligible cloud services with BAAs in place at the infrastructure level.
Network Isolation
PHI workloads run in dedicated VPCs with private subnets, network ACLs, and security groups that restrict traffic to explicitly authorized paths. No public internet exposure for data stores.
Infrastructure as Code
All infrastructure is provisioned through Terraform and/or AWS CloudFormation, delivering consistent, repeatable, and auditable configurations. No manual infrastructure changes in production.
Backup & Disaster Recovery
Automated encrypted backups with point-in-time recovery. Backup integrity is tested regularly, and recovery procedures are documented and rehearsed with defined RTOs and RPOs.
Cloud Provider BAAs
We maintain executed BAAs with our cloud infrastructure providers. All PHI workloads are deployed exclusively on HIPAA-eligible services within U.S. regions.

How ePHI moves through our systems
Data Ingress
TLS 1.2+ encrypted APIs
Encrypted Storage
AES-256 at rest, cloud-native KMS
Access Controls
RBAC + MFA, least privilege
Monitoring
Audit logs, SIEM, IDS
Encrypted Backups
Automated, tested, point-in-time recovery
Data Ingress
TLS 1.2+ encrypted APIs
Encrypted Storage
AES-256 at rest, cloud-native KMS
Access Controls
RBAC + MFA, least privilege
Monitoring
Audit logs, SIEM, IDS
Encrypted Backups
Automated, tested, point-in-time recovery
How does Digital Scientists use AI with our patient data?
Inside your environment, under your BAA, with a person approving every output. On new builds, models run through Amazon Bedrock in your own AWS account, covered by your BAA with AWS.
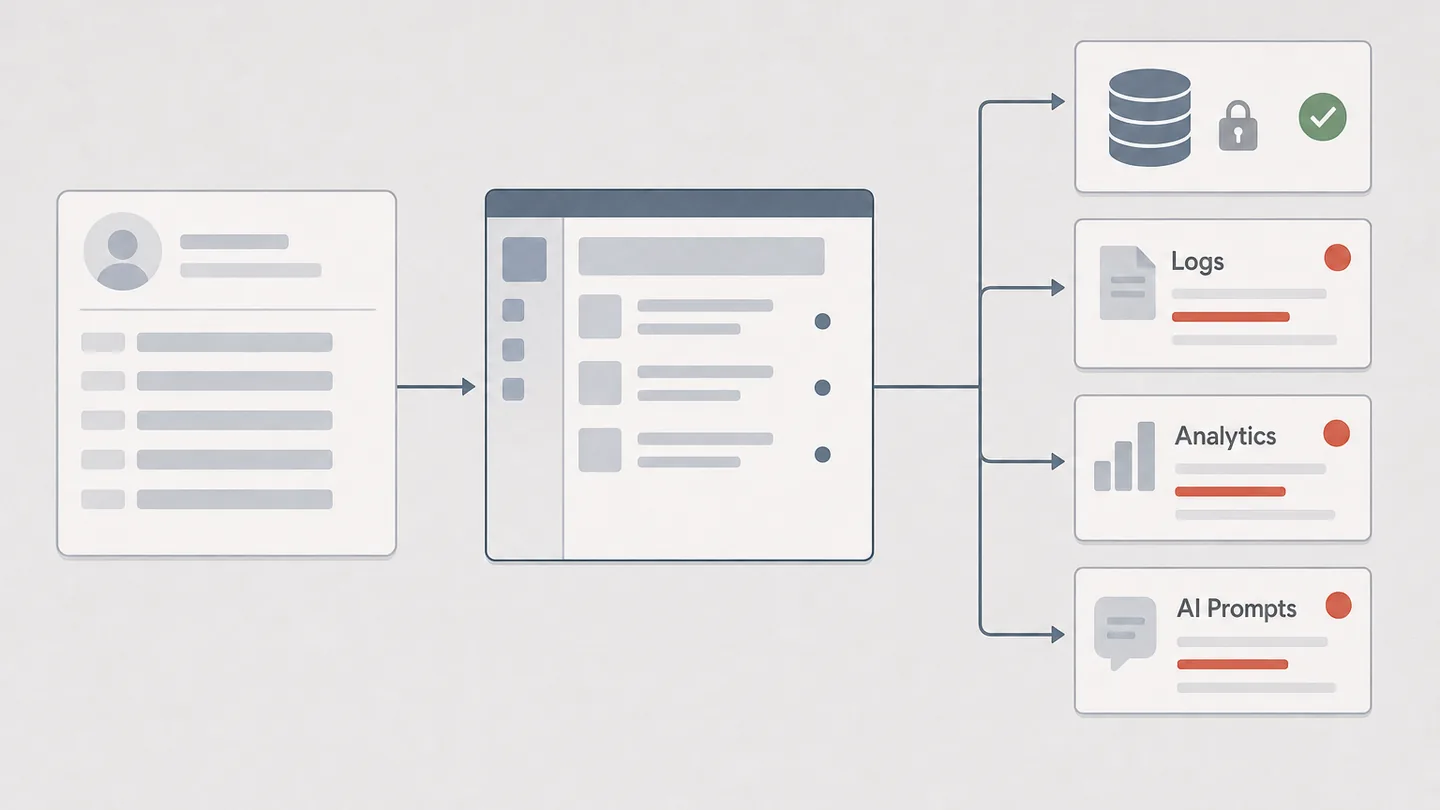
Protecting digital PHI gets harder once a model is in the loop. A reviewer's questions are fair ones: where does the data go, who sees the output, what happens when the model is wrong, and can you prove what it did six months later.
These four rules answer them. They come from production work. On CommuniCare's MDS platform, every recommendation links to its source documentation and an MDS coordinator validates it before acting. In risk adjustment, coders accept, change or reject every suggested code. Where a workflow needs patient consent, such as recording a visit for an ambient scribe, we build the consent step into the workflow.
Models run in your AWS account
On new builds, Amazon Bedrock runs inside your own AWS account, covered by your BAA with AWS. Your PHI stays in your environment and under your agreement.
Your data trains nothing for anyone else
We don't use your data to train models for any other client. Bedrock doesn't use your prompts or outputs to train the underlying models.
A person approves every output
A clinician, coder or reviewer approves each AI output before it's used. Nothing reaches the record on the model's say-so.
Every output is logged
On every build we log the input, the source it drew on, the model version and the reviewer's action. Any decision traces back.
Hybrid delivery under controlled access
Our delivery model separates security oversight from development execution, with consistent controls applied across all team members regardless of location.
US-Based Security Oversight
Security architecture and compliance decisions are led by our US-based team. This includes risk analysis, BAA execution, incident response, and all communication with your security and compliance stakeholders.
Controlled Production Access
All production access requires VPN, managed devices, and MFA. Every access event is logged and monitored. No team member accesses production systems from personal devices.
Role Separation
Development, test, and production access is separated by role. PHI access is granted per engagement and per individual. Developers working on non-PHI components do not touch production data.
Managed Under Strict Controls
Every team member operates under the same security policies, HIPAA training, background screening, and access controls. No exceptions.
What changes when our platform holds substance use disorder records?
Consent, redisclosure and record tracking change. 42 CFR Part 2 is the federal rule that protects records from federally assisted substance use disorder (SUD) treatment programs, and it sits on top of HIPAA.
The 2024 final rule brought Part 2 closer to HIPAA, with a compliance date of February 16, 2026. A patient can now sign one consent that covers treatment, payment and health care operations, and HIPAA breach notification now applies to Part 2 records. Consent still carries more weight than it does for other PHI. Every consented disclosure needs a notice, and SUD counseling notes need their own consent.
In software, the platform has to know which records are Part 2 and what each patient agreed to. We've run behavioral health workflows on NeverAlone since August 2023. When a build will hold Part 2 records, we design for it in the Blueprint, and the rules below go into the data model, the integrations and any AI that reads the record. See behavioral health.
How we design for 42 CFR Part 2
| Rule area | What Part 2 requires | How we design for it |
|---|---|---|
| Consent | Written patient consent for most disclosures. One consent can now cover future treatment, payment and operations. Patients can revoke it. | Consent stored as data, with scope, date and revocation. Every disclosure, export and feed checks it first. |
| Notice and redisclosure | Each consented disclosure carries a notice that limits redisclosure. Covered entities and business associates that receive records under a treatment, payment and operations consent can redisclose under HIPAA. | The notice travels with the disclosure. Outbound feeds filter on consent scope and the recipient's status. |
| Segmentation | The rule doesn't require separate storage, but you still have to know which records are Part 2. | Records tagged at intake by source program. Tags follow the data into reports, integrations and AI prompts. |
| SUD counseling notes | Need their own consent, separate from the general one. | A separate note type with its own consent check. |
| Legal proceedings | Records can't be used against the patient in civil, criminal or administrative proceedings without consent or a court order. | Legal requests route to your compliance team, and every access is in the audit log. |
| Breach notification | HIPAA breach notification rules now apply to Part 2 records. | Part 2 access sits in the same audit trail and incident response plan as other PHI. |
Your counsel decides how Part 2 applies to your program. We build the software to match that decision.
What security documents do you send during diligence?
We send a standard packet on request: the BAA, our security plan mapped to NIST CSF 2.0, a completed questionnaire and the rest of the documents below. It comes from our technical leadership, not a sales intermediary.
Most security reviews ask for the same evidence, so we keep it ready. Some documents are written for your project, so they arrive once we know the scope.
We don't hold SOC 2 or HITRUST, so neither report is in the packet. Your reviewer will find our controls in the security plan, the per-client addendum and the completed questionnaire, and can put follow-up questions to our engineers directly.
The diligence packet
| Document | What it covers | When you get it |
|---|---|---|
| Business Associate Agreement | Permitted uses, disclosure limits, safeguards, breach notification and subcontractor terms. Our standard template or yours. | Before any PHI is exchanged or system access is granted. Under one week from start to signature. |
| Security plan mapped to NIST CSF 2.0 | Our written information security program and HIPAA annex: policies, controls, roles and how we run them. | On request during evaluation. |
| Per-client security addendum | Where your project differs from our baseline: hosting, access, data handling, AI use and rules such as 42 CFR Part 2. | With the contract for the build. |
| Completed security questionnaire | SIG, CAIQ, HECVAT or your own format, from pre-filled answers we update quarterly. | On request during evaluation. |
| Architecture and data-flow diagram | A reference AWS architecture for HIPAA workloads. Then your system's architecture and PHI data flow. | Reference diagram on request. Yours as a Blueprint deliverable. |
| Incident response summary | Detection, escalation, notification within your BAA's timeframes, and post-incident review. | On request during evaluation. |
| Subprocessor list | Vendors and subcontractors that touch PHI on your project, each under a BAA. | On request, and with the security addendum. |
| Access rosters and audit logs | Who has access to your PHI, and what they did with it. | On request during the engagement. |
| Certificate of destruction | Written confirmation that copies of your data were destroyed. | On request when the engagement ends. |
No SOC 2 report or HITRUST letter is included, because we don't hold either.
We make your security review easy
We know what procurement and security teams need. Here is what we provide to move your evaluation forward.
Security Questionnaires
We complete SIG, CAIQ, HECVAT, and custom security questionnaires. Our responses are pre-filled and updated quarterly so turnaround is fast.
Architecture Diagrams
We provide network architecture, data flow, and system boundary documentation. Diagrams are engagement-specific and updated as systems change.
Data Flow Documentation
PHI ingress, storage, access, processing, and disposal are documented per engagement. We map every touchpoint where ePHI is handled.
BAA Templates
We provide a standard BAA template or work from yours. Turnaround is under one week from initiation to execution.
Pen Test Coordination
We coordinate with your penetration testing firm or share results from our most recent third-party assessment. We support scoped testing against staging or production environments.
Direct Technical Access
Your security team talks directly to our technical leadership. No sales intermediary. We answer architecture, compliance, and implementation questions in detail.
Platforms where we've protected PHI in production
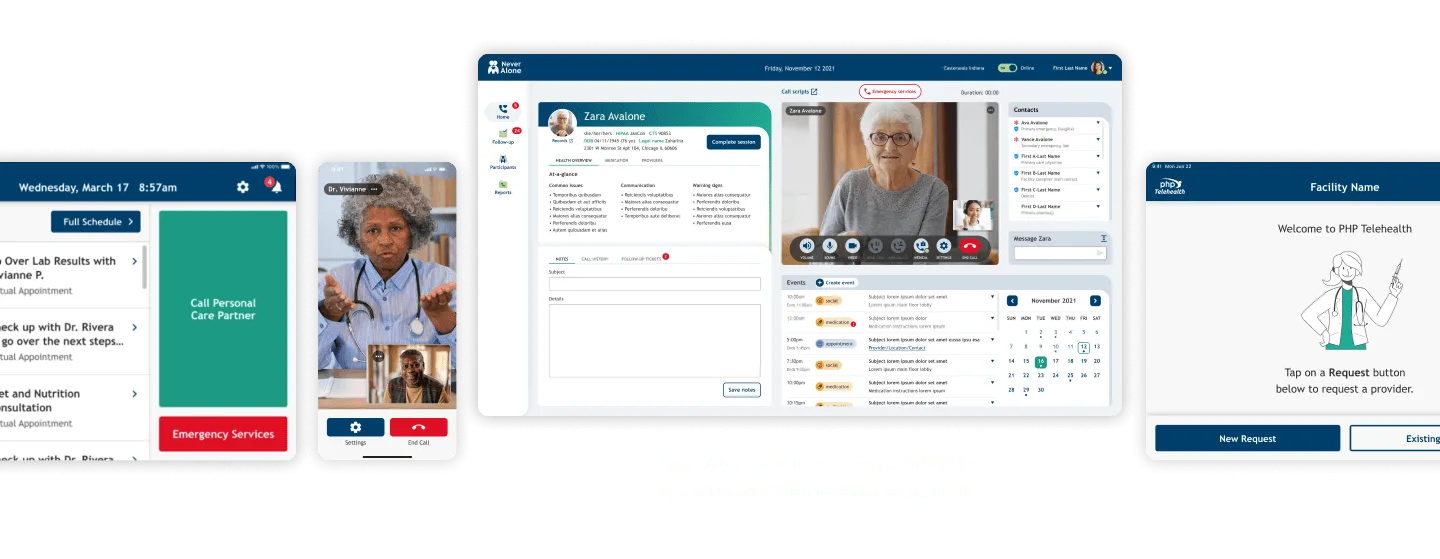
NeverAlone · CommuniCare
PHI in production since March 2021
A 24/7 virtual care platform for 30,000 patients across six states, with 100,000+ calls a year. We built it and we still run it.
See the work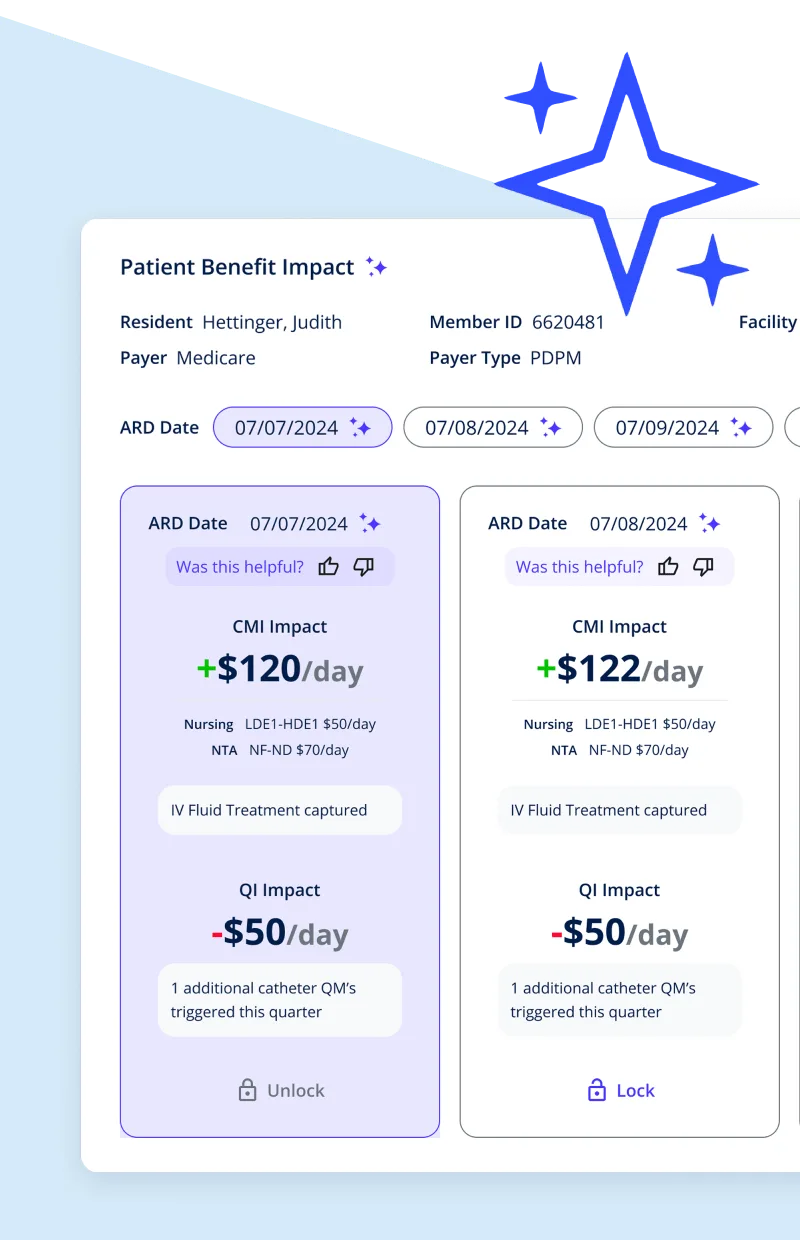
CommuniCare MDS
$10M+ recovered to date
AI recommendations on PointClickCare data, each linked to its source and validated by an MDS coordinator. $24M+ in forecast PDPM revenue. Built from April 2024 and handed to CommuniCare's own team.
See the work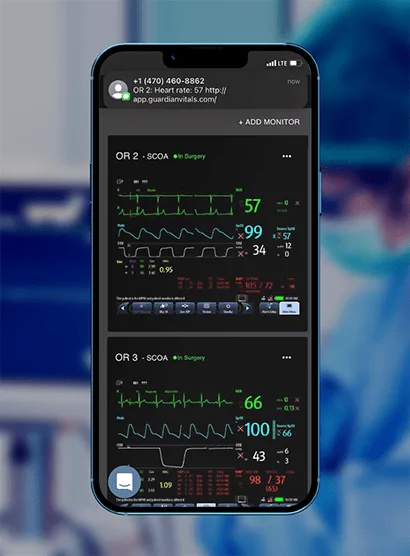
Guardian · Vigilant Medical
99.9% transcription accuracy
Vital signs streamed from operating room devices into an encrypted AWS environment built with Terraform, WAF, GuardDuty and CloudTrail.
See the workTrusted by healthcare leaders.
“I have worked with many technology teams during my career, and Digital Scientists is one of the best. They take the time to understand the customers' needs, deliver innovative solutions, are always professional, and work with your team as a true partner to achieve success.”

Amy Severino
Chief Innovation Officer, CommuniCare Health Services
“Digital Scientists provided immense value to our plan administrators, providers, and patients. The team was able to come in and understand our core needs, while remaining product agnostic. They helped identify the technical debt and pitfalls, and to get us to a point of stabilization and growth.”
Robert Hager
CEO, CommuniCare Advantage
Related healthcare services
Healthcare platform operations
We run the platforms we build, 24/7, with L2 and L3 support.
Healthcare platform operations →Cloud and HIPAA hosting
HIPAA-eligible AWS environments, built as code.
Cloud and HIPAA hosting →Healthcare integrations
EHR, lab, payer and claims connections that stay up.
Healthcare integrations →Healthcare AI development
On new builds, AI in your own AWS account, with a person approving every output.
Healthcare AI development →Ways to start
Common first steps, from a free conversation to a Blueprint.
Ways to start →Healthcare at a glance
What we build, who it's for and the proof, on one page.
Healthcare at a glance →Latest thinking on PHI and AI

Questions from procurement and security teams
Do you sign Business Associate Agreements?
Yes. We execute a BAA with every client engagement that involves PHI or ePHI, before any data is exchanged or system access is granted. We also maintain BAAs with our cloud providers and subcontractors.
Are you SOC 2 certified?
No. We don't hold a SOC 2 report, and SOC 2 isn't on our roadmap. We sign a BAA with every covered entity, run a security plan mapped to NIST CSF 2.0, and write a security addendum for each client's project. We are happy to share our current control documentation with prospective clients.
Where is PHI stored?
PHI is stored exclusively on HIPAA-eligible cloud services (AWS, Azure, or GCP depending on client architecture) within U.S. regions. All data stores are encrypted at rest, network-isolated, and access-logged. We maintain executed BAAs with all cloud infrastructure providers.
Who has access to production PHI?
Access is restricted to the minimum personnel required for the engagement, enforced through role-based access control and MFA. Access is logged, reviewed quarterly, and revoked immediately when no longer needed. We can provide access rosters and audit logs upon request.
What happens to our data when an engagement ends?
We follow a documented data return and destruction process defined in each BAA. Client data is returned in the format specified, and all copies are securely destroyed using methods appropriate to the storage medium. We provide written certificates of destruction upon request.
Have you experienced a PHI breach?
No. Digital Scientists has had no reportable breach of protected health information. We log every security incident, including ones where no PHI was exposed, and we'll walk your security team through that history. We maintain a documented incident response plan and conduct regular drills to verify our team can respond effectively if an incident occurs.
Can you complete our security questionnaire?
Yes. We regularly complete SIG, CAIQ, HECVAT, and custom security questionnaires. We maintain pre-filled responses that are updated quarterly. Contact us and we will coordinate with your security team.
What does HIPAA-compliant software development look like?
HIPAA-compliant software development integrates security and privacy controls at every stage of the SDLC. This includes threat modeling during design, secure coding standards, automated SAST/DAST in CI/CD pipelines, peer code review with security criteria, penetration testing, and production monitoring with audit logging. At Digital Scientists, every healthcare engagement starts with an executed BAA and follows our secure SDLC framework from day one.
How do you protect ePHI in a hybrid development team?
Security architecture and compliance oversight are US-based. All team members complete HIPAA training, background screening, and sign confidentiality agreements. Production access requires VPN, managed devices, and MFA. Access is role-separated so developers working on non-PHI components never touch production data. Every access event is logged and reviewed.
Will our data train your AI?
No. On new builds, models run through Amazon Bedrock in your own AWS account, covered by your BAA with AWS. Your data trains nothing for anyone else, and Bedrock doesn't use your prompts or outputs to train the underlying models. A clinician, coder or reviewer approves every AI output before it's used, and every output is logged with its input, source, model version and the reviewer's action.
Tell us what you're trying to do. Hear back today.
No commitment. No sales deck. We'll listen to your situation and recommend the right starting point, even if that means telling you we're not the right fit.